
Vulnerability Prioritization Overview
What is Vulnerability Prioritization?
GreyNoise Vulnerability Prioritization is intended to help customers get current, reliable, and actionable information about active exploitation of vulnerabilities on assets exposed to the Internet. Customers can use this information to prioritize mitigation and remediation of vulnerabilities that are truly urgent today.
Why Did We Build a Vulnerability Prioritization Product?
GreyNoise is uniquely positioned to offer timely and complete information about the active exploitation of a vulnerability in the wild. Most vulnerability management vendors get exploitation information from 3rd party sources that may be incomplete and can rapidly become out-of-date. GreyNoise shows exactly what attacks are happening on the Internet right now.
What data is included?
The full data dictionary for this endpoint can be found here
What should I do with this data?
The data provided for each CVE provides the unique insight that GreyNoise has to offer. This data can be used to
- Make prioritization decisions around patching known vulnerabilities
- Take a proactive stance around blocking IPs associated with these vulnerabilities at your perimeter
Blocking at the Perimeter
The CVE details page provides a Create Blocklist action when GreyNoise observes active exploitation.
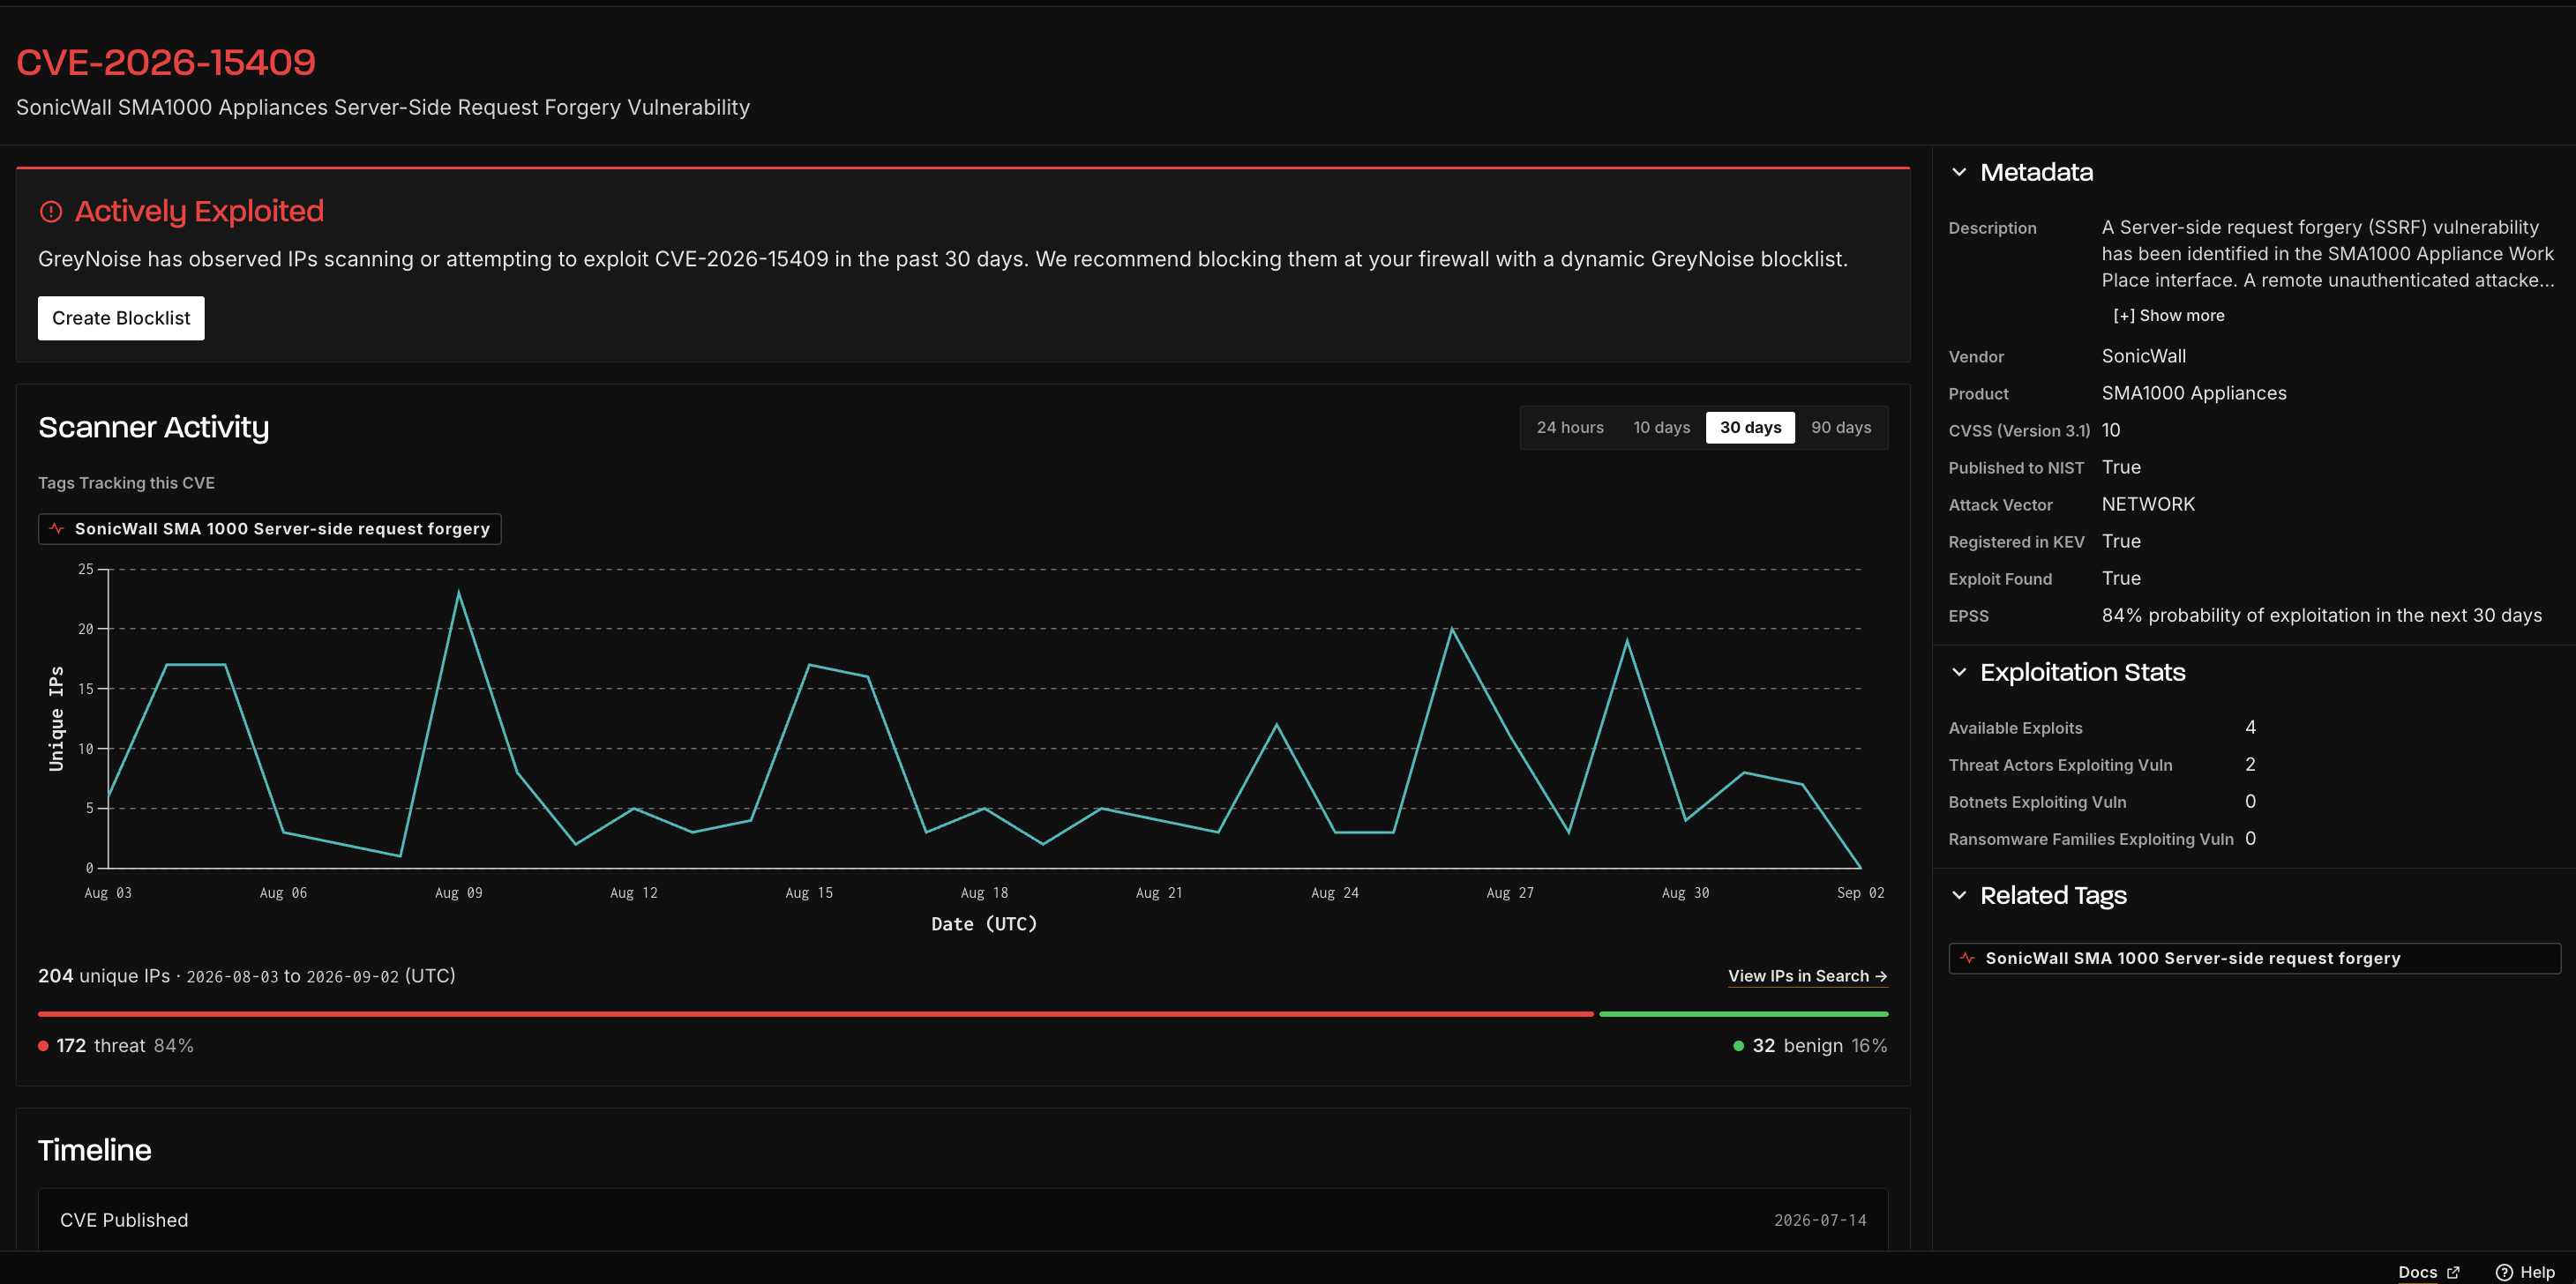
Once the blocklist is provisioned, configure its URL as a Firewall External Dynamic List (EDL) to proactively block all IPs associated with the CVE.
For more details on using GreyNoise Blocklists in Firewall Blocking, please see Firewall Blocking with GreyNoise Trends
Access Methods
Visualizer Access
Select CVEs in the Visualizer sidebar. The CVE catalog can be searched by CVE ID, vendor, or product. Select a result to open its details page, or open a known CVE directly, such as CVE-2024-24919.
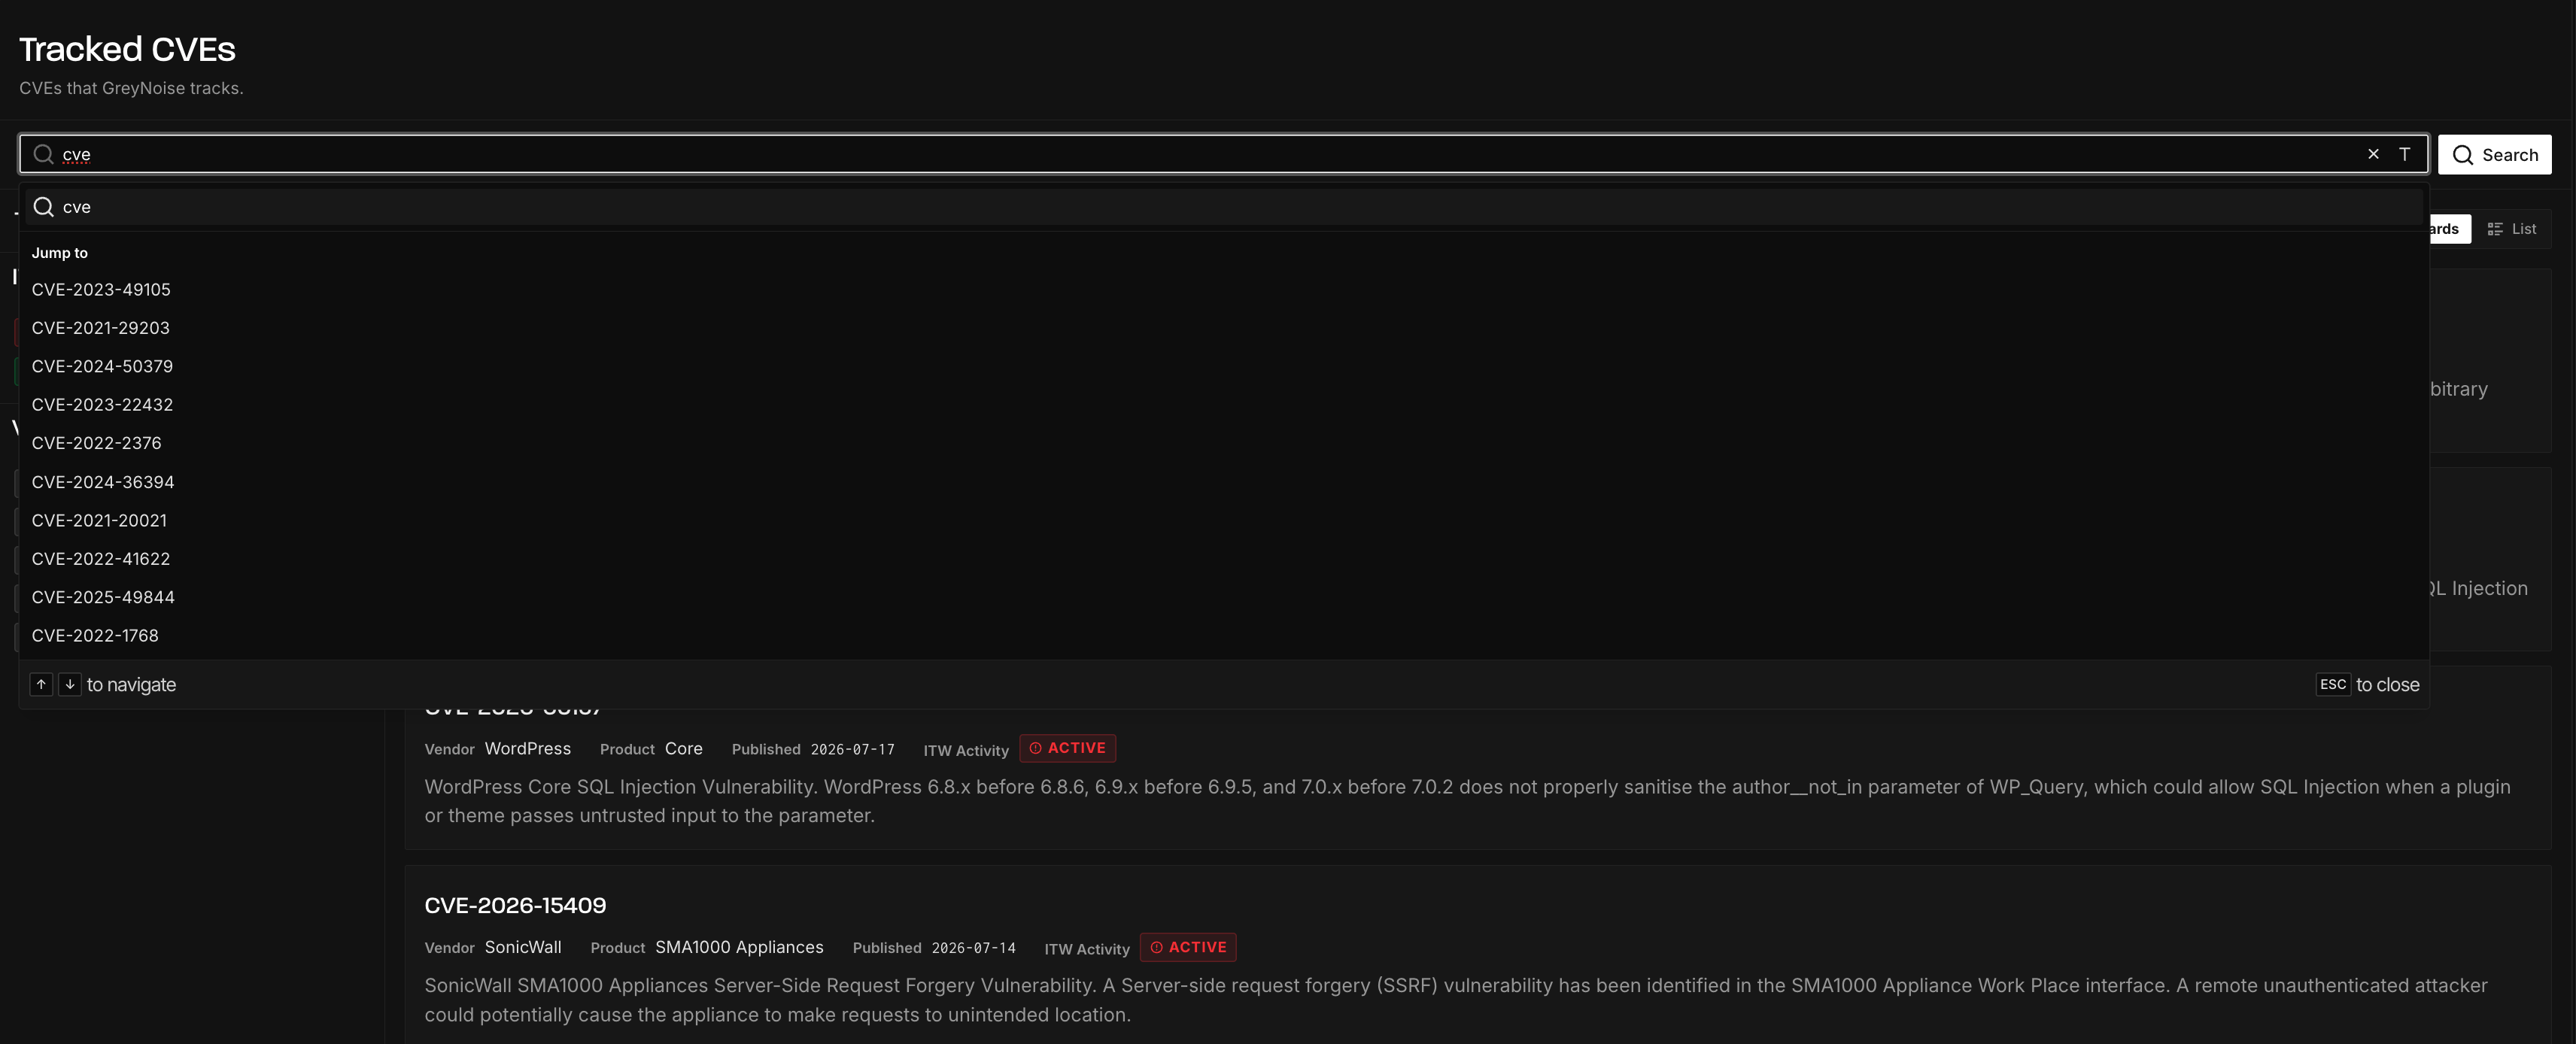
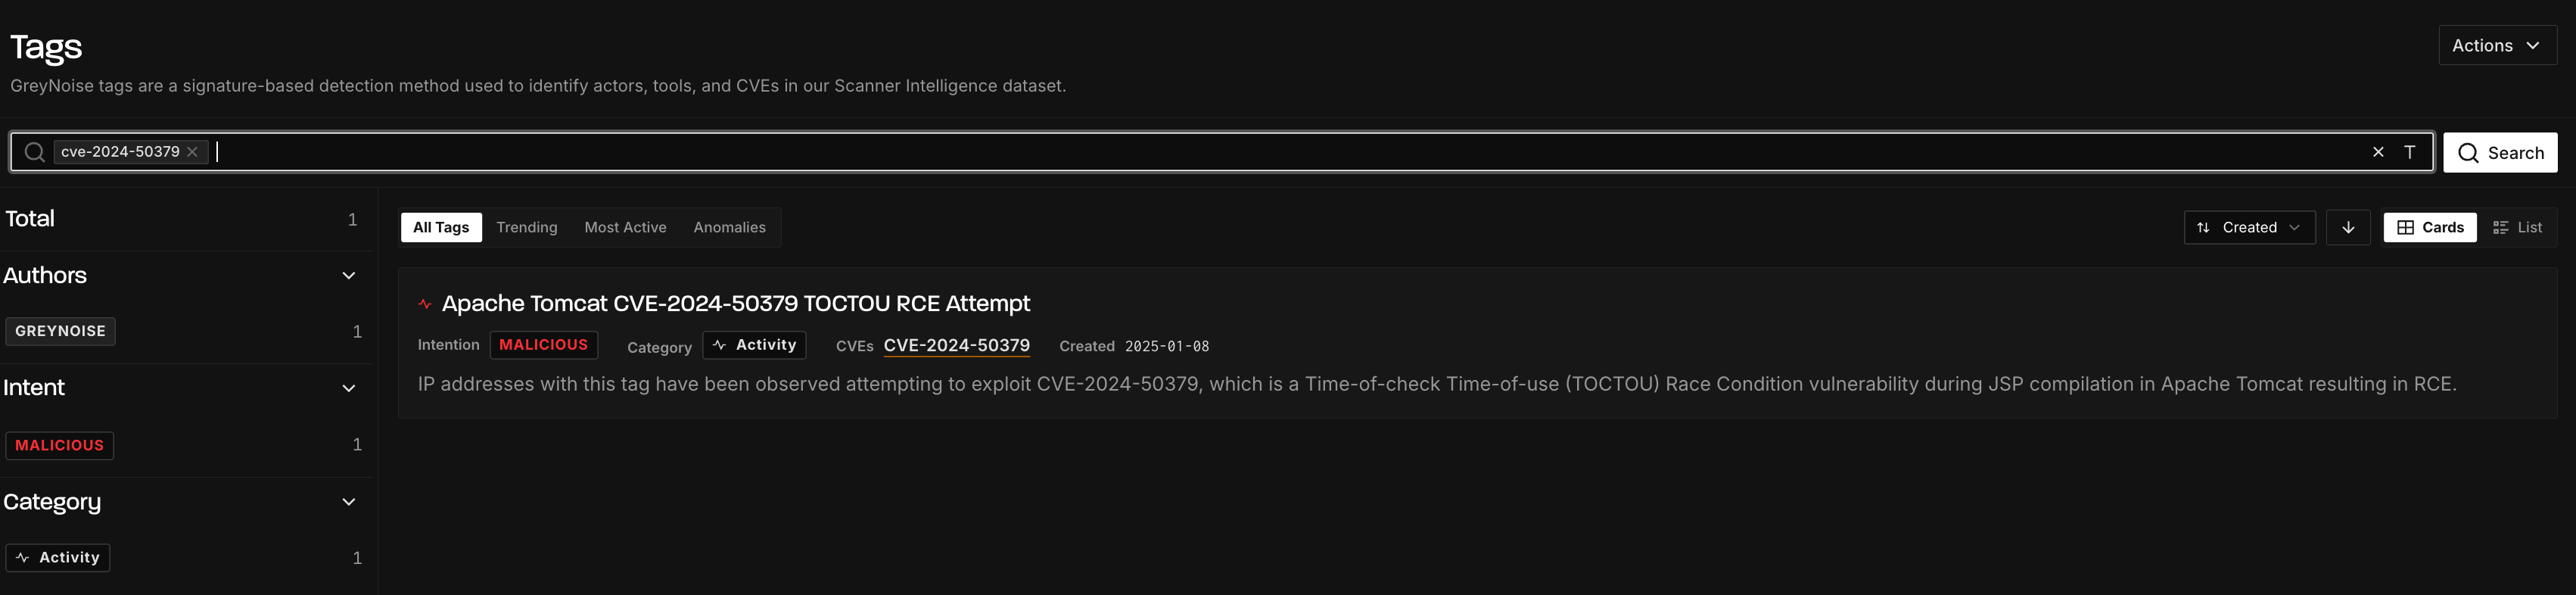
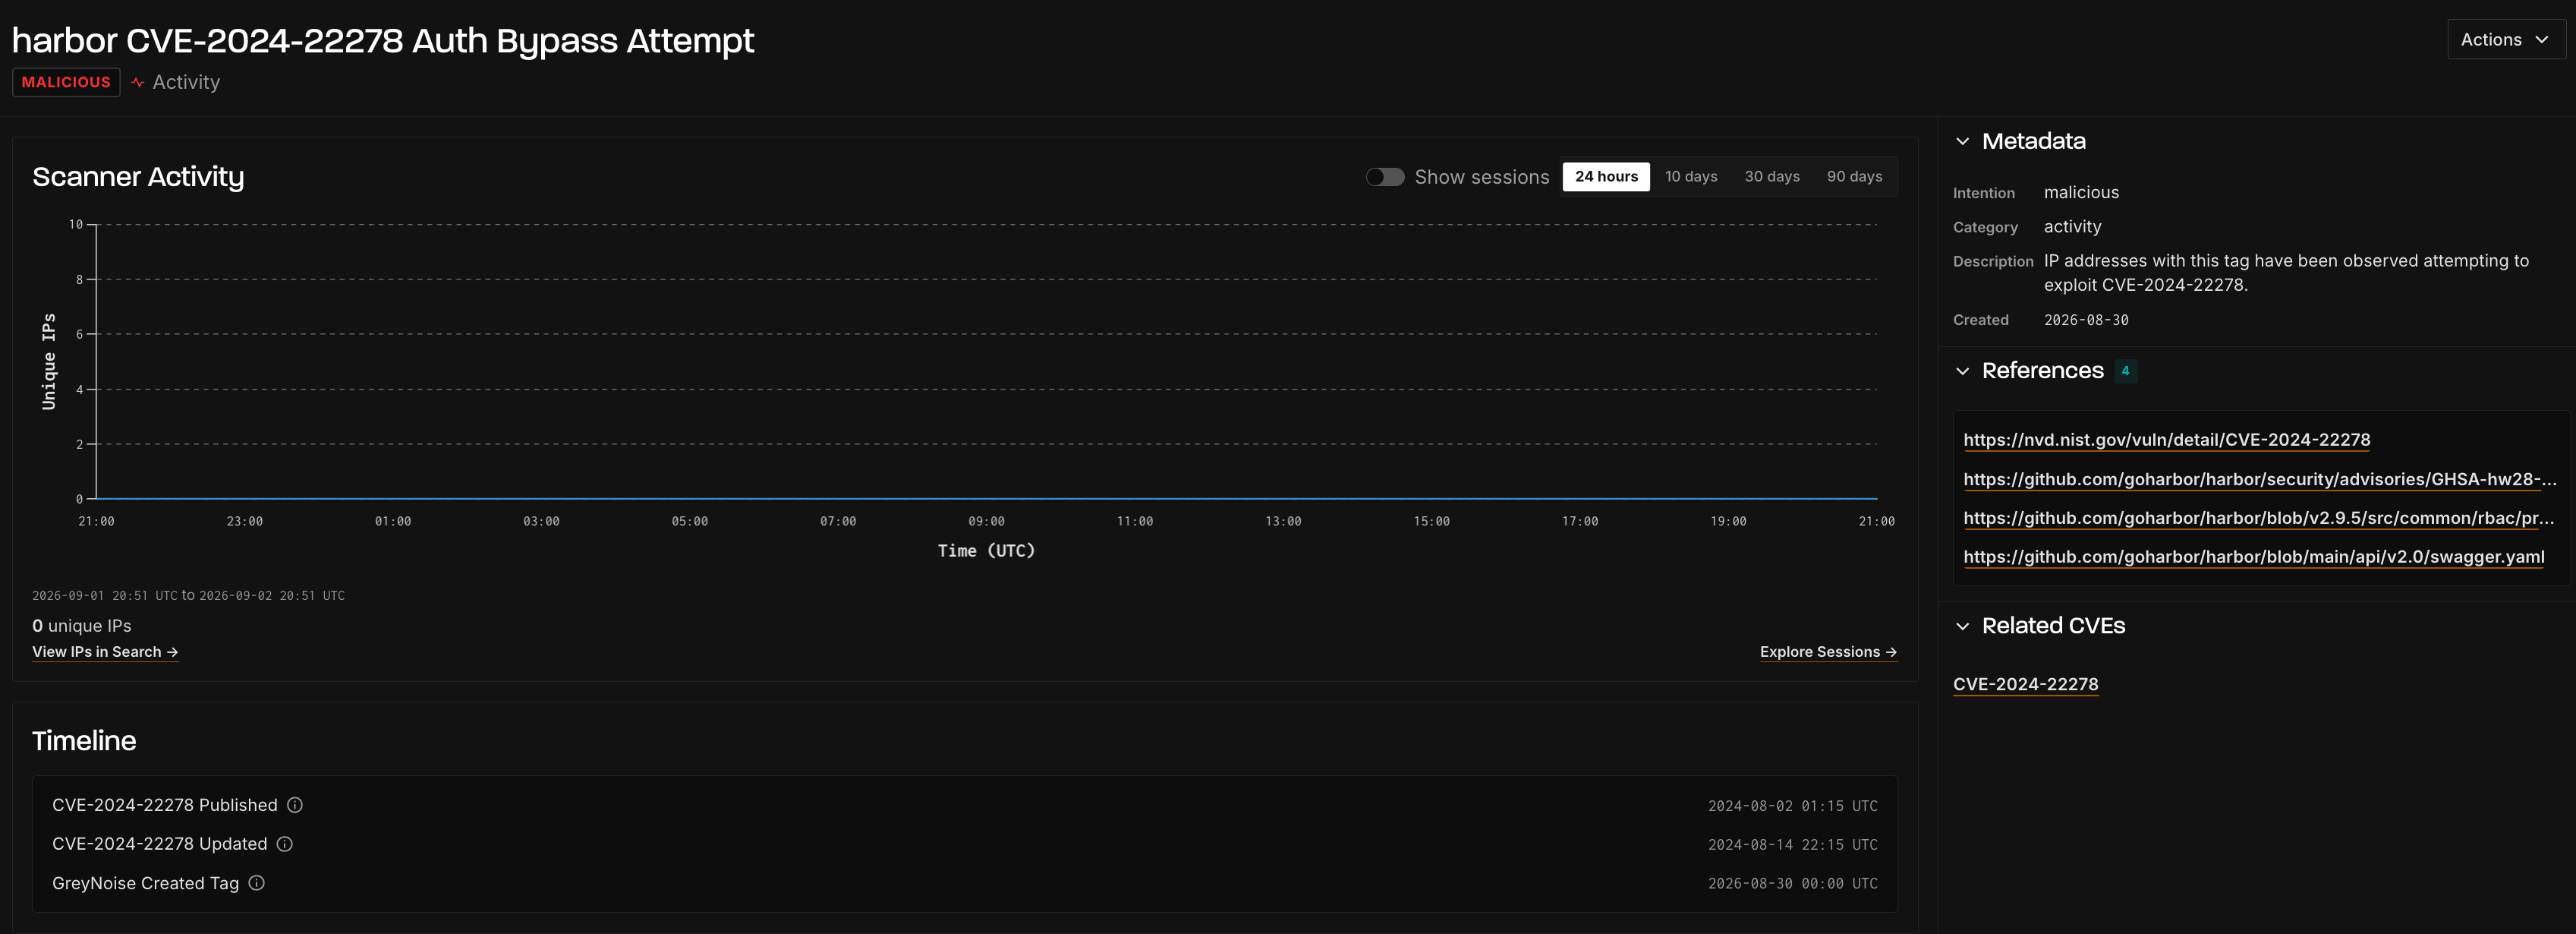
You can also open the sidebar search control, choose CVEs, and enter a CVE ID. From a tag details page, select a CVE under Related to open the same current CVE details page.
Vulnerability Prioritization Details Page
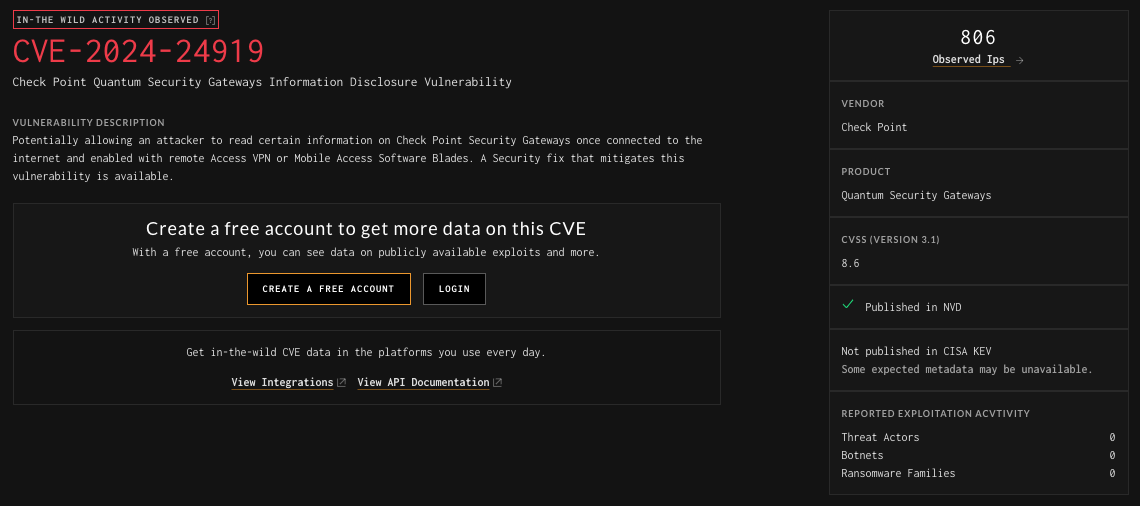
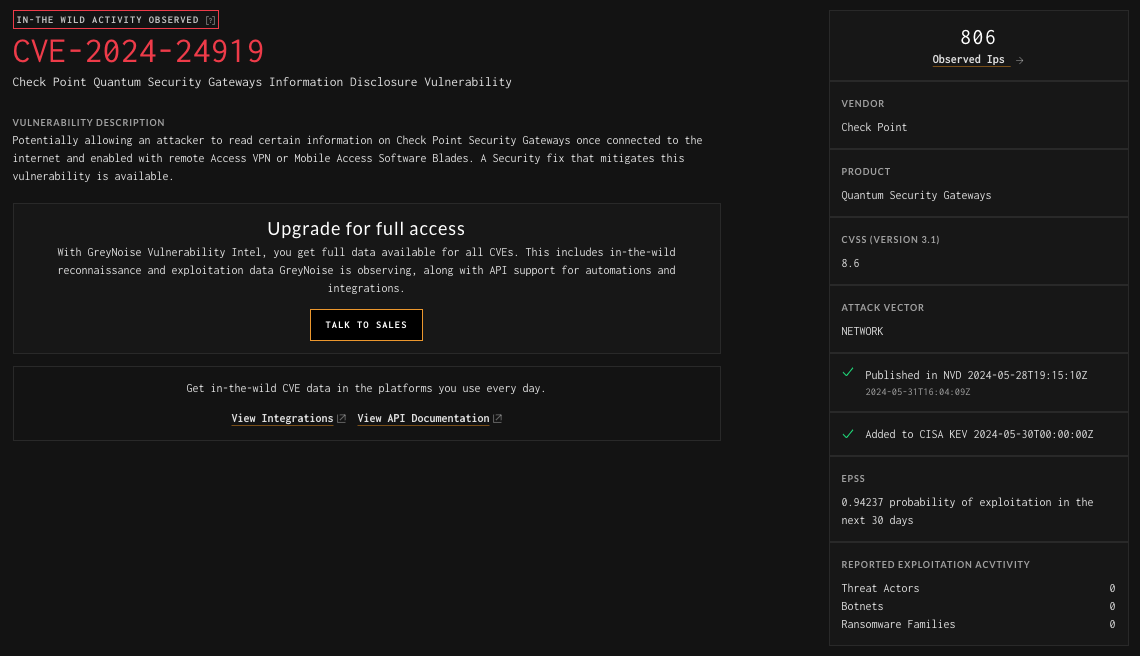
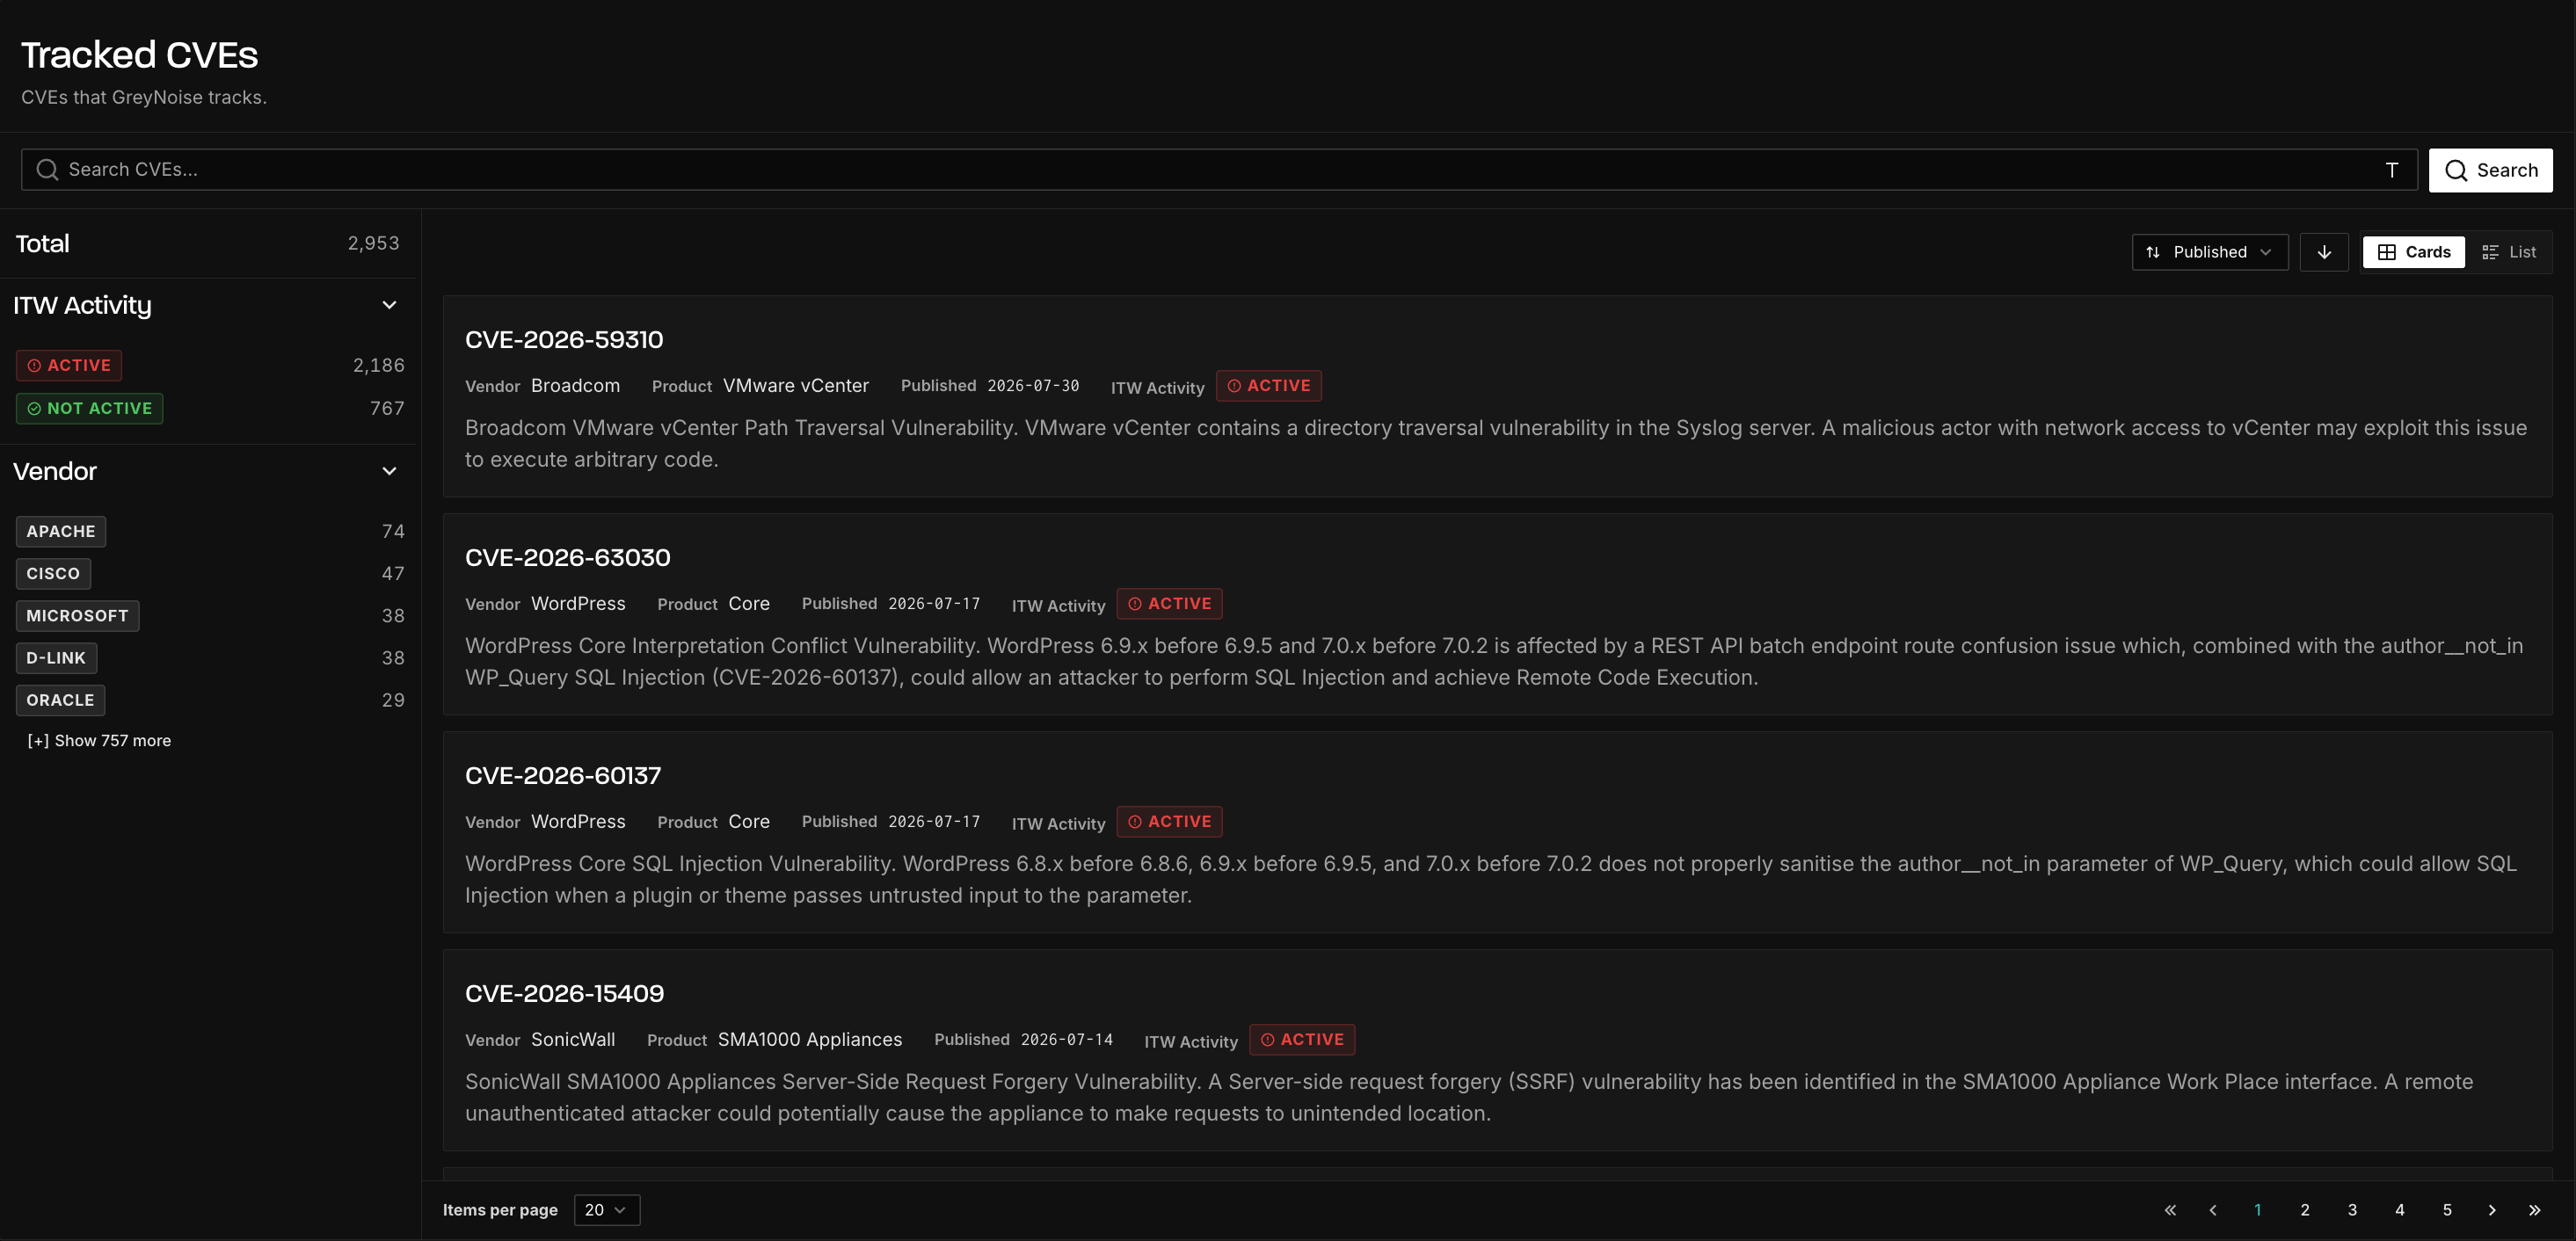
The details shown depend on your account and enabled intelligence modules. The page can include exploitation status, Scanner Activity, an exploitation timeline, metadata, exploitation statistics, related tags, and actions to create an alert or blocklist.
Vulnerability Prioritization API
Details on the API for the Vulnerability Prioritization Feature can be found here
Unauthenticated User Experience
{
  "id": "CVE-2024-24919",
  "details": {
    "vulnerability_name": "Check Point Quantum Security Gateways Information Disclosure Vulnerability",
    "vulnerability_description": "Potentially allowing an attacker to read certain information on Check Point Security Gateways once connected to the internet and enabled with remote Access VPN or Mobile Access Software Blades. A Security fix that mitigates this vulnerability is available.",
    "cve_cvss_score": 8.6,
    "product": "Quantum Security Gateways",
    "vendor": "Check Point",
    "published_to_nist_nvd": true
  }
}
Standard API Key User Experience
{
  "id": "CVE-2024-24919",
  "details": {
    "vulnerability_name": "Check Point Quantum Security Gateways Information Disclosure Vulnerability",
    "vulnerability_description": "Potentially allowing an attacker to read certain information on Check Point Security Gateways once connected to the internet and enabled with remote Access VPN or Mobile Access Software Blades. A Security fix that mitigates this vulnerability is available.",
    "cve_cvss_score": 8.6,
    "product": "Quantum Security Gateways",
    "vendor": "Check Point",
    "published_to_nist_nvd": true
  },
  "timeline": {
    "cve_published_date": "2024-05-28T19:15:10Z",
    "cve_last_updated_date": "2024-05-31T16:04:09Z",
    "first_known_published_date": "2024-05-27T00:00:00Z",
    "cisa_kev_date_added": "2024-05-30T00:00:00Z"
  },
  "exploitation_details": {
    "attack_vector": "NETWORK",
    "exploit_found": true,
    "exploitation_registered_in_kev": true,
    "epss_score": 0.94237
  }
}
Paid Subscription (with Vulnerability Prioritization SKU) User Experience
{
  "id": "CVE-2024-24919",
  "details": {
    "vulnerability_name": "Check Point Quantum Security Gateways Information Disclosure Vulnerability",
    "vulnerability_description": "Potentially allowing an attacker to read certain information on Check Point Security Gateways once connected to the internet and enabled with remote Access VPN or Mobile Access Software Blades. A Security fix that mitigates this vulnerability is available.",
    "cve_cvss_score": 8.6,
    "product": "Quantum Security Gateways",
    "vendor": "Check Point",
    "published_to_nist_nvd": true
  },
  "timeline": {
    "cve_published_date": "2024-05-28T19:15:10Z",
    "cve_last_updated_date": "2024-05-31T16:04:09Z",
    "first_known_published_date": "2024-05-27T00:00:00Z",
    "cisa_kev_date_added": "2024-05-30T00:00:00Z"
  },
  "exploitation_details": {
    "attack_vector": "NETWORK",
    "exploit_found": true,
    "exploitation_registered_in_kev": true,
    "epss_score": 0.94237
  },
  "exploitation_stats": {
    "number_of_available_exploits": 60,
    "number_of_threat_actors_exploiting_vulnerability": 1,
    "number_of_botnets_exploiting_vulnerability": 0
  },
  "exploitation_activity": {
    "activity_seen": true,
    "benign_ip_count_1d": 756,
    "benign_ip_count_10d": 756,
    "benign_ip_count_30d": 756,
    "threat_ip_count_1d": 2,
    "threat_ip_count_10d": 3,
    "threat_ip_count_30d": 6
  }
}
Updated 15 days ago